The CISO's Guide to AI Security for Business Leaders
By Yonatan Hoorizadeh CISSP, CISM, CRISC, AAISM
Published By: Purple Shield Security
Published: August 10, 2026
Last updated: August 10, 2026
AI security fails at most companies because AI risk gets classified by tool name rather than by what the system can reach and whether its actions can be undone. Sort every AI system you run into four exposure tiers, then match controls, framework work, and insurance disclosures to the tier. Classification comes before governance.
Why does AI security keep failing at companies with solid IT?
AI security fails at well-run companies because the classification is wrong before any control gets chosen. Most businesses sort AI risk by product name and ask whether Microsoft Copilot is safer than ChatGPT. The question that actually predicts incidents is different: what data and systems can this AI reach, and can a person undo what it does? Companies that skip the second question end up governing high-consequence systems the way they govern a chat window.
The drift usually happens in three quiet steps. A tool gets approved in the first quarter as a drafting assistant with access to nothing. In the second quarter, someone connects it to the shared drive so it can answer questions about internal documents. In the third quarter it gets permission to call other systems: create tickets, send messages, update records. The approval record still describes the first quarter version, and so does the security policy that was written against it.
The scale of that gap is now measurable. The Cloud Security Alliance and Token Security surveyed 418 IT and security professionals for a report published on April 21, 2026 titled Autonomous but Not Controlled. It found that 82 percent of organizations had discovered AI agents running in their environments that their security, IT, or governance teams did not know about. In the same survey, 68 percent said they had strong visibility into the AI agents on their network.
Those two numbers are the whole problem in one line. Confidence tracks what leadership approved. Exposure tracks what actually got deployed. Hillary Baron, assistant vice president of research at the Cloud Security Alliance, framed the fix as moving governance toward a more unified, operational model that can sustain control at scale.
In practice, the fastest way to find the difference between the two is not a scan. It is asking finance to pull twelve months of corporate card statements and expense reimbursements and sorting them for AI vendors. Departments buy AI on a card long before IT hears about it, and the accounting system is the only place that record survives.
What is actually going wrong with AI right now?
AI incidents in 2026 are mostly not exotic attacks on models. They are ordinary access-control failures wearing new clothes. IBM's 2026 Cost of a Data Breach Report, released July 29, 2026, found that among organizations breached through an AI model or application, the most common entry points were compromised APIs, applications, or plug-ins at 27 percent, and cloud misconfigurations affecting AI workloads at 27 percent. The AI did not fail. The plumbing around it did.
The cost figures explain why boards are now asking about this. The same IBM report, conducted with the Ponemon Institute across 602 organizations breached between March 2025 and February 2026, found that one in four malicious breaches were AI-enabled, a 56 percent increase over the prior year. Those breaches averaged $6 million, roughly $1 million above the $4.99 million global average. The US average across all breaches reached $11.5 million.
Suja Viswesan, vice president of IBM Security Software, described the shift bluntly: AI is making attacks faster and cheaper, while breaches keep getting more expensive. That asymmetry is why the economics have moved, and it is the argument that lands with a CFO when a technical explanation does not.
Shadow AI is now a first-order cost driver rather than a policy annoyance. As Cybersecurity Dive reported from the 2026 IBM findings, the share of security incidents involving shadow AI more than doubled year over year to 43 percent, and more than two-thirds of organizations said they had no governance process in place to limit it.
There is also a revealing gap in how companies deploy AI defensively. IBM found that more than half of organizations use AI agents for threat detection and containment, but only 18 percent apply them to vulnerability management. Detection has the budget. Remediation, which is where the exposure window actually closes, does not.
On the agent side, the consequences are already concrete. In the Cloud Security Alliance and Token Security research, 65 percent of organizations reported at least one AI agent-related security incident in the past twelve months. Of those incidents, 61 percent involved data exposure or mishandling of sensitive data, 43 percent caused operational disruption, and 35 percent produced financial losses. Only 21 percent of organizations had a formal process for decommissioning an AI agent.
That last number is the one most coverage skips, and it creates what the researchers call retirement debt: agents that outlived their purpose but kept their credentials, their permissions, and their access. Three patterns show up repeatedly in assessments. First, the agent nobody turned off, still holding a token issued eighteen months ago. Second, the vendor you never onboarded, which is an AI feature switched on by default inside a SaaS product you already pay for. Third, the permission nobody scoped down, where an integration was granted write access during setup because read-only broke something on a Friday.
For engineering teams that want shared vocabulary, the OWASP GenAI Security Project published the OWASP Top 10 for Agentic Applications 2026, catalogued as ASI01 through ASI10, covering agent goal hijack, tool misuse, memory poisoning, and rogue agents. It is useful precisely because it was built from observed incidents rather than projections.
The four AI exposure tiers: how to classify what you already run
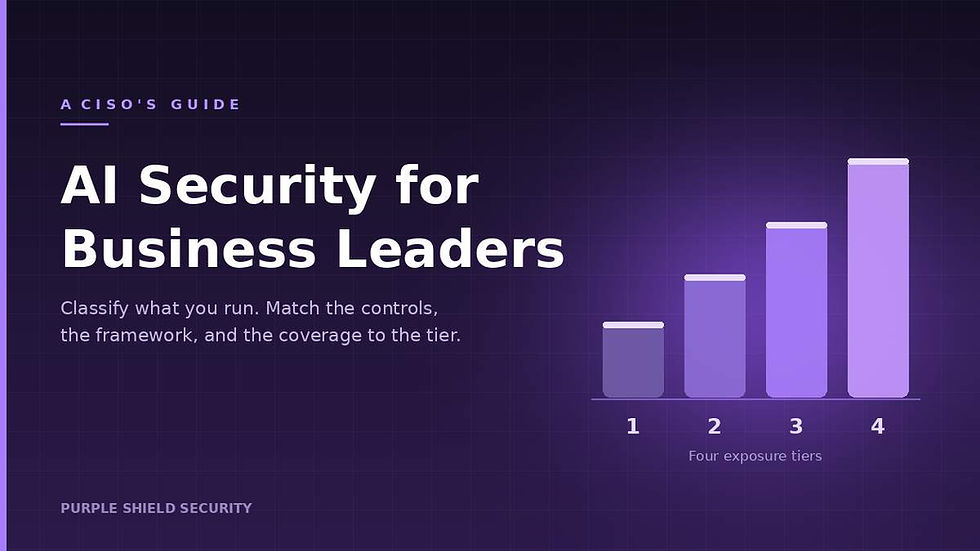
Sort every AI system in your company along two axes: reach, meaning what data and systems it can touch, and reversibility, meaning whether a person can undo its actions before consequences land. Those two axes produce four exposure tiers. The tier, not the vendor's brand, should determine what controls, documentation, and insurance disclosures attach to a system.
Tier 1, Assistive
A Tier 1 system reads or drafts, touches only public or low-sensitivity information, and produces nothing that leaves the company without a person reviewing it first. A marketing manager using a public chatbot to draft a first pass at a newsletter is Tier 1. The dominant risk is data leakage through what employees paste into the prompt. The control that matters is a sanctioned tool plus an acceptable use policy people have actually read, because employees denied a sanctioned option will use an unsanctioned one.
Tier 2, Embedded
A Tier 2 system has standing access to internal or regulated data but still only produces output a person acts on. Microsoft Copilot indexed across a SharePoint tenant is Tier 2. So is an AI notetaker sitting in every client call, or a support assistant reading your full ticket history. The risk shifts from what employees paste to what the system can already see. The control that matters is permission scoping on the underlying data, because these tools surface everything the account can reach, including files that were overshared years ago and never noticed.
Tier 3, Actuating
A Tier 3 system takes actions in live systems, but those actions are reversible and rate-limited. An agent that updates CRM records, tags and routes tickets, schedules meetings, or opens pull requests for human review is Tier 3. The risk becomes identity. The control that matters is giving the agent its own identity with its own scoped, short-lived credentials, rather than running it on a shared API key, a generic service account, or a departed employee's login.
Tier 4, Consequential
A Tier 4 system takes actions that move money, change access rights, alter production data, or produce a decision about a person in employment, credit, housing, insurance, or care. The risk is now legal and financial, and often irreversible. The control that matters is a human approval gate on the specific irreversible action, a kill switch someone has actually tested, and a written record of who authorized the deployment. Tier 4 is also where the AI-specific employment and consumer protection laws start to bite.
The rule that resolves most arguments is this: a system sits at the highest tier it can reach, not the tier it was purchased at. If a Tier 1 assistant is granted a connector that lets it write to a system, it became a Tier 3 system that day, and the paperwork should change the same week. The single most common finding in an AI security assessment is a Tier 3 or Tier 4 capability operating under a Tier 1 approval, usually because nobody re-reviewed the tool after an integration was switched on.
Tier 1, Assistive. Drafting and summarizing on public or low-sensitivity data, reviewed by a person. Control that matters: a sanctioned tool plus a read acceptable use policy.
Tier 2, Embedded. Standing access to internal or regulated data, output still acted on by a person. Control that matters: permission scoping on the underlying data.
Tier 3, Actuating. Reversible, rate-limited actions in live systems. Control that matters: its own identity with scoped, short-lived credentials.
Tier 4, Consequential. Moves money, changes access rights, alters production data, or decides about a person. Control that matters: a human approval gate, a tested kill switch, and a written authorization record.
Tiering is unglamorous work, and it is also the step that makes everything downstream cheaper. Controls, framework alignment, vendor questionnaires, and insurance disclosures all key off the same classification. Firms that buy AI security services before they have a tiered inventory usually end up paying for monitoring on systems that should simply have been turned off.
Do the 2026 AI regulations actually apply to my business?
Most of the AI-specific laws businesses spent 2025 preparing for have been delayed, narrowed, or rewritten. That is not a reason to stand down, because the binding constraints on a typical US company were never the AI statutes. They are the sector law you already live under, the terms in your customer contracts, and the exclusions in your insurance policy. Those three moved faster than any legislature.
In Europe, the Digital Omnibus on AI was endorsed by the European Parliament on June 16, 2026, given final approval by the Council on June 29, 2026, and entered into force in July 2026. It deferred the high-risk obligations for standalone Annex III systems from August 2, 2026 to December 2, 2027, and for AI embedded in regulated products under Annex I to August 2, 2028.
What did not move is the part most services businesses will actually touch. The Article 50 transparency obligations, covering chatbot disclosure, deepfake labeling, and marking of synthetic content, applied on schedule on August 2, 2026. Generative systems already on the market before that date have until December 2, 2026 to meet the machine-readable marking requirement. Coverage that summarized all of this as the EU delaying the AI Act was half right and operationally misleading.
In the United States, Colorado's SB 24-205 never took effect at all. Its start date slipped from February 1, 2026 to June 30, 2026, a federal court paused enforcement on April 27, 2026, and SB 26-189, signed May 14, 2026, repealed and replaced it with a narrower statute governing automated decision-making technology, with duties beginning January 1, 2027.
Several state laws are in force today and get far less attention. Texas TRAIGA (HB 149) took effect January 1, 2026, though the final version was cut down to prohibited uses and rules for state agencies rather than a broad high-risk regime. Illinois HB 3773 took effect January 1, 2026 and amends the Illinois Human Rights Act to reach employer use of AI that discriminates against protected classes. California's AB 2013 training data disclosure and SB 53 also took effect January 1, 2026, alongside California Privacy Protection Agency rules on automated decision-making tools and Civil Rights Council regulations on employment screening.
Here is the practical read for a US company under a few thousand employees. If AI touches hiring, promotion, or termination anywhere in your process, you are regulated today under Illinois and California rules, regardless of what happens to the AI-specific statutes still in flux. If you sell into the EU or your output is used there, the transparency obligations already landed. Everything else on the list is a 2027 problem you should be building toward rather than a 2026 deadline you missed. That distinction is worth getting right, because the delays produced a wave of executives who concluded, incorrectly, that nothing applies to them.
Why your insurance carrier is regulating AI faster than any legislature
Your insurance carrier is setting AI security requirements faster than any legislature, and those requirements bind you contractually in a way that guidance never does. In January 2026, Verisk's Insurance Services Office division put three generative AI exclusion endorsements into circulation for commercial general liability policies. The forms are optional. Carriers decide whether to attach them at your renewal, and many are.
The three forms do different amounts of damage. CG 40 47 is the broad one, excluding bodily injury, property damage, and personal and advertising injury arising out of generative AI under both Coverage A and Coverage B. CG 40 48 is narrower, excluding only Coverage B, which is the personal and advertising injury bucket that catches defamation and advertising-related IP claims. CG 35 08 applies the exclusion to products and completed operations.
The operative language is arising out of, which courts read broadly. A claim does not have to be primarily about AI for the exclusion to be argued. A defamation claim over AI-drafted marketing copy, an infringement claim over an AI-generated image, or a liability claim where an AI recommendation played some role can all land inside it.
Joe Lam, vice president of liability at Verisk and one of the people who wrote the endorsements, told Claims Journal in July 2026 that carriers have shown a high degree of interest whenever a new endorsement is introduced. Adoption is not uniform. W.R. Berkley has filed an absolute AI exclusion reaching directors and officers, errors and omissions, and fiduciary lines, and other carriers have filed their own wording rather than adopt the standard forms. The result is that no two policies now treat AI the same way.
Affirmative coverage exists on the other side of the market. Coalition added an affirmative AI endorsement to its cyber policy, HSB launched an AI liability product aimed at small and mid-size businesses in March 2026, and Armilla wrote a standalone AI liability policy at Lloyd's. What these have in common is that underwriters generally want to see documented AI governance before granting them.
Anyone who renewed a cyber policy between 2019 and 2022 has seen this film. Multi-factor authentication went from a recommendation, to a question on the application, to a condition of coverage, and some claims were contested over how that question had been answered. AI governance is walking the same path on a shorter timeline. The consequence for a business owner is specific and easy to miss: your AI inventory has stopped being an internal security document and become an insurance representation. If the application asks where you use AI and the answer is incomplete because nobody ever built the inventory, that is not only a control gap. It is a disclosure problem, and disclosure problems are what carriers litigate.
Four questions are worth putting to your broker before you bind a renewal. Which endorsement form numbers are attaching to the general liability policy? Does the cyber policy affirmatively cover AI-driven attacks, including funds transfer triggered by a deepfake instruction? Is affirmative AI coverage available as a write-back or a standalone policy? And what governance documentation would the underwriter need to see in order to grant it?
ISO 42001 or NIST AI RMF: which does a mid-market company actually need?
For most mid-market companies the answer is the NIST AI Risk Management Framework now, and ISO 42001 only when a customer starts asking for the certificate. ISO/IEC 42001:2023 is the first certifiable AI management system standard, published in December 2023, with 38 Annex A controls across nine objectives and a Statement of Applicability that decides which apply to you. The NIST framework is voluntary, free, and maps onto security work you are probably already doing.
ISO 42001 is structured like ISO 27001, using the same clause layout, so companies already certified will find it familiar. Europe adopted it as EN ISO/IEC 42001:2026. The friction is real, though: qualified lead auditors who understand both AI systems and management system governance remain scarce, and the documentation has to stay current as models, architectures, and use cases change. It is an ongoing commitment rather than a project with a finish line.
The NIST AI Risk Management Framework 1.0, released January 26, 2023, organizes around four functions: Govern, Map, Measure, and Manage. One detail deserves more attention than it gets. Alignment with the NIST AI RMF provides an affirmative defense under Texas TRAIGA. That is a rare case of a voluntary US framework carrying direct statutory weight, and it makes NIST alignment cheap insurance for companies with any Texas exposure.
NIST is also building Control Overlays for Securing AI Systems, known as COSAiS, which adapt SP 800-53 controls to AI-specific concerns across four use cases: generative AI assistants, predictive AI, single and multi-agent systems, and AI developers. The concept paper landed in August 2025 and the first overlays are still in draft as of mid-2026. If you already run a NIST-based program, this is the track worth watching, because it will let you extend existing controls rather than start a parallel framework.
The decision rule most companies need is short. If you build or sell AI features into enterprise, healthcare, or financial services buyers, and procurement teams are already asking for governance evidence, ISO 42001 is a sales investment with a governance byproduct, and it is worth being honest about that ordering. If you use AI but do not build it, run NIST AI RMF alignment mapped onto your existing NIST CSF 2.0 or SOC 2 work and do not open a certification project. And if you are in a regulated sector already, remember that HIPAA, GLBA, and PCI DSS still govern the data. AI does not create a separate compliance universe. It creates a new place where the same regulated data now lives, which is exactly what a risk assessment should be scoped to find.
Who owns AI risk when your company has no CISO?
AI risk is unowned at most companies, which is precisely why it accumulates. In survey data published by Gravitee in June 2026, only 7.2 percent of organizations reported having a named individual with formal accountability for AI agent behavior. Roughly a third described accountability as unclear or situation-dependent, and another 30 percent described it as shared but not formally defined. Diffuse ownership means nobody has the standing to say no.
The structural reason is that AI enters a company through four doors at once. Procurement signs the contract but never sees the permission scope. IT administers the tenant but was not on the vendor call. Legal reviews the data processing terms but does not know the tool was later connected to the CRM. The business unit sees the productivity gain and has no incentive to go looking for the exposure. Each function holds a fragment. None holds the whole picture.
Whoever owns AI risk has to be able to do five specific things: maintain the inventory, set and enforce the tier thresholds, stand behind the answers on the insurance application, approve or block a deployment on their own authority, and own the record when something goes wrong. The fourth one is where most arrangements quietly fail. Plenty of companies have someone tracking AI usage. Far fewer have someone who can stop a deployment that a revenue-generating department wants.
Most companies in the 50 to 500 employee range cannot justify a full-time chief information security officer and do not need one. What they need is the seat filled by someone with the standing to use it. That is the practical case for fractional CISO services: a senior security executive who holds the accountability, works a defined number of days per month, and reports at a level where a no actually holds. For AI specifically, vCISO services tend to be more useful than a one-time assessment, because AI exposure changes every time somebody enables a connector. A report written in March describes a system that no longer exists in June.
One structural point is worth saying out loud, because it rarely is. The party classifying your AI exposure should not also be the party selling you the AI platform, the security tooling, or the managed service that runs it. An AI security consultant with reseller relationships has a legitimate business model and a genuine conflict at the exact moment your tiering decision determines what you buy. Ask any AI security consulting firm you speak with how they are compensated and whether they hold vendor agreements with the products they recommend. Purple Shield Security is structured without product resale or referral fees for that reason, and the same question is worth asking of anyone else you evaluate. The answer tells you what the assessment is really for.
What should a business do in the next 90 days?
Ninety days is enough time to go from no AI governance to a defensible position, provided you sequence it correctly. The order matters more than the effort: inventory first, classification second, controls third, and documentation last, because every later step depends on knowing what you actually run.
Days 1 through 30 are for the inventory, and it should not be built from a survey alone. Pull twelve months of corporate card and expense data and sort for AI vendors. Export the application list from your identity provider or single sign-on tool. Open the admin console of every major SaaS platform you use and check which AI features are enabled by default, because several vendors have turned them on without a separate purchase. Then ask department heads directly. The Cloud Security Alliance finding is the reason survey-only inventories fail: the systems you do not know about are, by definition, the ones nobody will volunteer.
Days 31 through 60 are for tiering and for closing the mismatches it exposes. Anything landing at Tier 3 or Tier 4 needs three things before the window closes: its own identity with scoped credentials, a human approval gate on any irreversible action, and a named owner who is a person rather than a department. Anything you cannot find an owner for should be turned off. Decommissioning has the worst adoption rate of any control in this space at 21 percent, and it is also the cheapest risk reduction available, because a retired agent has no attack surface.
Days 61 through 90 are for producing the two artifacts that have value outside your own building. The first is a written AI governance policy that names the tiers, the approval path, the accountable individual, and the exception process. The second is an inventory you would be comfortable attaching to an insurance application or a customer security questionnaire. Both are being asked for now, by underwriters and by enterprise procurement teams, and both take weeks to produce under pressure and days to produce calmly.
One thing to skip: do not start with a tool purchase. Every AI security platform on the market is priced against an inventory you do not have yet, and buying detection before you know what exists produces a dashboard full of findings nobody has the context to act on. Classification is the cheap step that makes the expensive steps optional.
Frequently asked questions
Does the EU AI Act apply to my US company if I do not sell in Europe?
Usually not, if you have no EU users, no EU customers, and no output used in the EU. The scope test turns on where the AI system's output is used rather than where your company is incorporated, so a US professional services firm delivering AI-assisted work product to an EU client can be in scope. The obligations most likely to reach a US services business are the Article 50 transparency rules, which applied on August 2, 2026 and cover disclosing that content or a chatbot is AI-generated.
Will our cyber policy cover an incident caused by an AI agent?
Read the endorsement schedule rather than the coverage summary. Look for form numbers CG 40 47, CG 40 48, and CG 35 08 on general liability, and search every liability policy for the phrase generative artificial intelligence, since some carriers use proprietary wording instead of the standard forms. Affirmative AI coverage is available from several carriers as a write-back endorsement or a standalone policy, but underwriters typically require documented governance before granting it.
Do we need ISO 42001 certification, or is a written policy enough?
If no customer or regulator is asking for the certificate, a written policy plus a maintained inventory plus NIST AI RMF alignment is enough, and it costs a fraction as much. Pursue ISO 42001 when procurement teams start requiring it in deals you want to win, which is happening first in enterprise software, healthcare, and financial services supply chains. Treat the timing as a sales decision informed by risk, not the reverse.
How is AI security different from the cloud security we already do?
The controls overlap more than most vendors admit. IBM's 2026 report found the leading causes of AI-related breaches were compromised APIs, applications, or plug-ins and cloud misconfigurations affecting AI workloads, both of which are cloud security problems with familiar fixes. What is genuinely new is autonomy: an agent can chain actions across multiple systems faster than a person can review them, which is why the approval gate on irreversible actions matters more than any perimeter control.
At what size does a company actually need an AI security consultant?
Size matters less than tier. A twelve-person company running a Tier 4 system that touches payments or hiring decisions carries more real exposure than a three-hundred-person company where AI is used only for drafting. The trigger is not headcount. It is the first time an AI system is permitted to take an action that nobody reviews before it commits.
AI exposure is not a technology problem you solve once. It moves every time an employee enables an integration, a vendor ships a new feature, or a department signs up for something on a card. If you want help building the inventory, tiering what you find, and producing governance documentation your underwriter and your enterprise customers will accept, Purple Shield Security provides AI security services and vCISO leadership to businesses that need the accountability filled without adding a full-time executive. Independent, vendor-neutral, and no products to sell you.